

Create, Manage and Distribute Policies with Ease
Draft, approve and distribute policies, assign them by location, and track who has acknowledged each one. Built for multi-location operators — and you can sign up and see plans without booking a call, which most of this category will not let you do.
Policy management software controls the whole life of a written policy: drafting, review, approval, distribution, acknowledgment, revision and retirement. What separates one product from another is rarely the editor — it is what the system can still prove about a policy two years later, when the person who wrote it has left and an auditor asks which version was in force in March.
What policy management software is
Policy management software is a system for creating, approving, distributing and tracking an organisation’s written policies and procedures, with a record of who was given each policy, which version they were given, and when they confirmed they had read it.
It differs from a shared drive in one specific way: a shared drive stores the current file, while a policy management system stores every version of the file plus the evidence of who saw which one.
Most organisations arrive here from the same place. Policies live in a folder structure that made sense to whoever built it, the current version is whichever file has the latest date in its name, and proof that staff read anything is a spreadsheet someone maintains by hand. That works until it has to be defended.
The failure is rarely the writing. It is that the organisation cannot reconstruct, after the fact, what it told people and when. A policy management system exists to make that reconstruction routine rather than forensic.
Why operators pick PolicyTrak
Most of this category is built for a head office with an org chart. PolicyTrak is built for an operator with sites. Policies are assigned by location rather than by department, acknowledgment is tracked per person and per site, and you can sign up and see plans today without booking a call.
Every platform in this category will store a policy and collect a signature. The differences that decide a shortlist are narrower and more practical than the feature lists suggest. Here are the four we would put our own name behind, each one checkable against published documentation rather than a claim you have to take on trust.
1 · You can start without a sales call
Of the ten platforms we reviewed, eight quote only on request and several gate even a look at the product behind a demo booking. PolicyTrak lets you sign up and see plans the same day. That alone removes two weeks from most evaluations.
2 · Assignment is shaped like an operator, not an org chart
Bulk assignment to multiple sites and auto-assignment for new locations. Acknowledgment status is readable per location, not only as an organisation-wide percentage. Competitors that publish per-location assignment mostly express it as departments or regions.
3 · Version history that genuinely goes back
Every revision is kept with the name of the person who made it and the time it was saved. Nothing is overwritten, any earlier version opens and reads in full, and two versions can be set side by side. This is the capability we would most readily put in front of an auditor.
4 · Drafting and import in the same place as the record
Drafting and PDF import mean the policies you already have come in without retyping, and from that point they carry a version history and an approval record rather than sitting in a folder beside them.

Source Published documentation and pricing pages of PolicyTrak, PowerDMS, NAVEX PolicyTech, DocTract, ConvergePoint, VComply, PolicyStat, Ntracts Policy Manager, Trainual and SweetProcess. Verified September 2026. Where a vendor does not publish something we record it as not stated, never as absent.
The six stages of the policy lifecycle
A policy passes through six stages, and a gap at any one of them breaks the chain of evidence: draft, review, approve, distribute, acknowledge, then revise or retire. Most tools handle three or four of these well and leave the rest to email.
The two highlighted stages are where the evidence is created, and they are the two most often handled outside the system. A policy emailed as an attachment has been distributed in a sense that satisfies nobody later.
The evidence chain
What an auditor asks for is rarely the current policy. It is the one that was in force at the time: what the document said on a given date, who changed it, and when. That is a question about version history, and it is the link most systems answer worst.
What has to connect for a policy record to hold
Each box is a link in the chain. The labels beneath it are what has to be recorded for that link to survive questioning.
AI-powered policy creation
Draft policies in minutes, not hours. For busy compliance teams, creating comprehensive policies from scratch is time-consuming. PolicyTrak’s AI-assisted drafting helps you produce a thorough first draft quickly — which you then review, route for approval and version like any other policy.
- Smart Templates — start with industry-specific templates that cover common compliance requirements.
- AI Content Generation — describe what you need and let AI generate a complete policy draft for review.
- Grammar and spelling check — built-in AI editing keeps policies polished and professional.
- PDF import and extraction — upload existing policy PDFs and let AI extract and format the content automatically.

A drafting assistant is a starting point, not a compliance decision. Whatever a template or a generated draft produces still needs review by someone who knows your obligations, and the approval workflow below is where that review gets recorded.
Version control and history
PolicyTrak stores every revision as a numbered version, with the name of the person who made it and the date and time it was saved. Nothing is overwritten. Any earlier version can be opened and read in full, and two versions can be displayed side by side to show exactly what changed between them.
This is the part of the category that is easiest to describe and hardest to retrofit. A system that keeps only the current document can tell you what a policy says. It cannot tell you what it said, which is the question that actually gets asked.
Automatic version tracking
Every save creates a new version with timestamps and user attribution.
Compare versions
View side-by-side comparisons to understand exactly what changed between versions.
Rollback capability
Restore previous versions if needed, with full audit trail preservation.
Change summaries
AI-generated summaries explain what changed in each version.
| What is recorded | What that lets you answer later |
|---|---|
| Numbered version | Which iteration of this policy are we discussing |
| Author name on each revision | Who made this change |
| Date and time of each save | When the wording changed |
| Full earlier versions, retained | What the policy said on a given date, without reconstructing it |
| Side-by-side comparison | Exactly what changed between two versions, rather than an assertion that something did |
| Audit log entry per change | Whether the change was to the content, the delivery method or the status |
Source PolicyTrak product behaviour, verified September 2026.
Approval workflows
Ensure proper review before distribution. Critical policies shouldn’t go live without oversight. PolicyTrak’s approval workflow puts the right people in front of a policy before it reaches employees, and records that they were.
- Custom approval chains — define who approves a policy based on category, department or sensitivity.
- Status tracking — see where each policy sits in the approval process.
- Approval notifications — automatic reminders to approvers when a policy is waiting on them.
- Audit records — a complete record of who approved what, and when.
The acknowledgment record
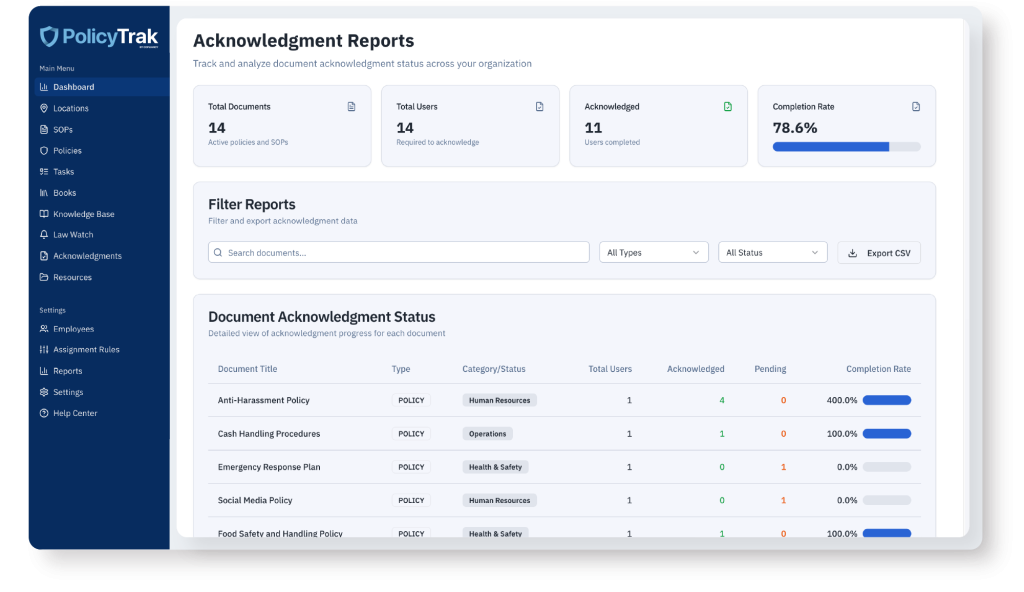
The employee types their full name and confirms, as a distinct act rather than as a by-product of closing the document, and the confirmation is recorded with its date. Status is readable per person and per location, so you can see who is outstanding rather than only an organisation-wide percentage. Policies reach people three ways: in the app, by email with the document attached, or by an emailed one-time link.
The difference between an explicit act and an implied one matters more than it first appears. A system that treats closing a document as agreement has recorded that a file was opened. A system that requires a deliberate confirmation has recorded a decision. Which of the two you have is the thing that gets tested.
What gets questioned later is never the policy. It is the record of who was told, and what the system can still show about it.
The practical test of a policy programmeWhat that record establishes in any particular dispute is a question for counsel rather than for a software vendor. What the platform does is capture it and keep it. For what the federal ESIGN Act and the state-level UETA say about electronic signatures, and the records that support one, see our guide to e-signature compliance. For how acknowledgment status is tracked across locations, see policy acknowledgment tracking.
Source PolicyTrak product behaviour, verified September 2026.
Location-based assignment
The right policies reach the right locations. A policy can be assigned to some sites and not others, and acknowledgment status is visible by employee and by location rather than only as an organisation-wide total.
Multi-site organisations are where most policy programmes come apart, because the audience for a policy is rarely everyone. A food-safety procedure binds the kitchen, not the corporate office. A state-specific rule binds three sites out of eleven. A system that can only publish to the whole organisation pushes that distinction back into email, which is where the evidence trail ends.
Bulk assignment
Assign policies to multiple locations at once instead of repeating the same distribution site by site.
Auto-assignment
New employees receive the policies that apply to their location as part of onboarding rather than as a separate manual step.
Jurisdiction awareness
Policies can be assigned according to the state, county or city requirements they were written for. Whether a given rule applies to your operation is a determination for your own advisers, not one the software makes.
Business type filtering
Filter the library by the type of operation a site runs, so a location is not issued procedures written for a different kind of site.
Source PolicyTrak product behaviour, verified September 2026.
PDF export and distribution
Policies leave the system in a form other people can read and file. Any policy can be exported as a formatted document and sent on — which is what an auditor, a franchisor or an insurer usually asks for.
One-click PDF generation
Produce a formatted PDF of any policy as it currently reads, or of an earlier version held in the history.
Custom headers and footers
Carry your own branding, document reference and version marker onto the exported file.
Batch export
Export a whole library, or a filtered set, in one operation rather than a document at a time.
Email distribution
Send policies directly from the system, so the distribution is recorded alongside the document instead of sitting in someone’s sent items.
Export matters for a reason that is easy to miss at evaluation: the record has to survive leaving the platform. If the only readable form of an acknowledgment report is a screen inside a tool you may not be using in five years, the retention question is still open. See also retiring and archiving outdated policies.
Source PolicyTrak product behaviour, verified September 2026.
See the record a policy leaves behind
A walkthrough of the version history, the acknowledgment record and the reports, on your own policies rather than a demo library.
Book a walkthroughPolicy management vs document management vs GRC
The three categories overlap and are routinely sold against each other. Document management stores and versions files. Policy management adds distribution to a defined audience and proof of receipt. GRC platforms add risk registers, controls testing and regulatory mapping on top of both.
| Capability | Document management | Policy management | GRC platform |
|---|---|---|---|
| Stores files with version history | ✓ | ✓ | ✓ |
| Approval workflow before publication | sometimes | ✓ | ✓ |
| Distribution to a defined audience | — | ✓ | ✓ |
| Per-person acknowledgment record | — | ✓ | ✓ |
| Risk register and controls testing | — | — | ✓ |
| Regulatory mapping | — | partial | ✓ |
| Typical buyer | IT or operations | HR, compliance or operations | Risk or internal audit |
Note These are category boundaries, not product claims. Individual products cross these lines in both directions. The footer bar indicates relative breadth of scope, not a score.
Most organisations that believe they need a GRC platform need policy management and a spreadsheet. Most that believe a shared drive is enough discover otherwise during their first audit.
PolicyTrak sits squarely in the middle column, and deliberately so: the full policy column without the risk-register apparatus that makes a GRC platform an implementation project. If you need controls testing and a risk register, buy a GRC platform. If you need the right policy in front of the right people at the right sites, with a record that survives questioning, that is the problem we built for.
Questions to ask any vendor before buying
Eight questions that separate a system which holds a record from one which merely displays documents. Ask them of us as readily as of anyone else.
- Show me a policy as it read eighteen months ago. Not the change log — the document itself. If that takes more than a few clicks, the version history is decorative.
- Show me what changed between two versions. A side-by-side comparison, not a note saying the policy was updated.
- How is a person without a company email address given a policy? Ask every vendor. None of the ten we examined publishes an answer.
- Can a policy be assigned to three sites out of eleven? And can outstanding acknowledgments be seen for just those three?
- What exactly does the acknowledgment record contain? Identity, timestamp, and which version was presented, at minimum.
- Who maintains any regulatory content you supply, and how current is it? Ask for the update cadence and who reviews it. Only two of ten publish a maintained content library at all.
- What does it cost at our headcount in eighteen months? Per-user and per-organisation pricing diverge sharply as an organisation grows.
- What happens to the records if we leave? Export format, ownership, and retention after cancellation.
If you are building the shortlist rather than the questions, what to include in a policy change log covers the record an auditor actually reads, and creating a policy exception register covers the gap between what the policy says and what the organisation does.
Related reading
Policy distribution and tracking
Sending a policy to a defined group, and recording per person and with a date that they confirmed reading it.
Policy version control
Every revision kept as a numbered record with its author and timestamp, readable in full, comparable side by side and restorable.
Policy approval workflows
How a policy moves from draft to in force, and what the record should show about who authorised each step.
Policy acknowledgment tracking
How acknowledgment records are captured, tracked across locations and exported.
E-signature compliance: ESIGN and UETA
What the statutes say about an electronic signature, and the records that support one.
What to include in a policy change log
The trigger, the rationale, the approval and the impact — and how auditors use them.
Retiring and archiving outdated policies
What to archive, what to tell affected staff, and why the old version still matters.
Creating a policy exception register
Recording the exceptions you have formally granted, and stopping policy drift.
Reducing policy sprawl
Consolidating a bloated library without losing required coverage.
Frequently asked questions
What is policy management software?
How is it different from document management software?
Can employees without a company email address acknowledge policies?
Is the acknowledgment tied to the specific version the employee saw?
What does the version history actually keep?
Can a policy be assigned to some locations but not others?
How much does policy management software cost?
Glossary
A recorded confirmation by a named individual that they have received and read a specific policy, with a date attached.
Used interchangeably with acknowledgment by most vendors. Some reserve it for confirmations carrying an additional declaration, such as confirming no conflict of interest.
Retaining each revision of a document as a distinct, retrievable item rather than overwriting the previous text.
The chronological log of actions taken on a policy — edits, approvals, distributions, acknowledgments — each with an actor and a timestamp.
The gradual divergence between what policies say and what the organisation actually does, usually through accumulated informal exceptions.
The accumulation of overlapping, redundant or obsolete policies that enlarge the library without adding coverage.
The date from which a policy binds, which is not always the date it was approved or the date it was distributed.
Formally ending a policy while retaining it in an archive, because the period it governed remains open to examination.
Ready to get started?
Sign up and see plans today — no call required — or book a walkthrough on your own policies. Either way you will know within an hour whether the record it keeps is the one you need.
Sign Up for Free → Book a Demo